

Agentic security for an agentic threat
inforcer Agentic TDR moves at machine speed, correlating signals across the tenant, recognizing abnormal patterns, building context, and auto-containing threats before they spread. It then prevents the same attack across your entire customer base.
Threats are inevitable. We stop them faster.
-
0 secondsMicrosoft 365 session hijackedinforcer Agentic TDR: Awaiting log from M365Human-led SOC: Awaiting alert
-
26 secondsOptions to move laterally across the tenant identifiedinforcer Agentic TDR: Logs received and threat raisedHuman-led SOC: Awaiting alert
-
29 secondsAttempting to access mailboxesinforcer Agentic TDR: Threat contained, PSA alert raisedHuman-led SOC: Awaiting alert
-
1 minuteAuthentication failedinforcer Agentic TDR: Report to prevent threat for all users generatedHuman-led SOC: Awaiting alert
-
5 minutesAuthentication failedHuman-led SOC: Alert received, waiting to be triaged to human
-
1 hourAuthentication failedHuman-led SOC: Alert picked up
-
1.5 hoursAuthentication failedHuman-led SOC: Threat contained

*Stats based on the fastest response time seen so far.
Human SOCs can’t keep up
Finding and correlating threats manually can take hours, if not days or months. But the agentic attacks we see today happen in seconds.
Humans can’t:

Review every incident
See the pattern across thousands of signals
Act at 2am
Your peers are already stopping agentic threats
How our MSP partners are using inforcer Agentic TDR to detect, contain, and remediate incidents faster and keep pace with agentic threats.
-
“Before inforcer, we were doing TDR manually. We didn’t really know we could save 3-4 hours per ticket. Before, they had to manually go through, download each log, run that log through a different system and now it’s all automated."
Stephen Mykel,
Director of IT Operations, Pacific Office Automation
-
"I loved the AI analyzer. The timeline is chronological and the contain, remediate, and advise options are really clear. For a lot of MSPs, this would be a perfect product."
Ruben Ven,
Modern Workplace Consultant, Yellow Arrow
-
"inforcer TDR is plugging a real gap between unmonitored alerts and our expensive 24/7 service. The value-add of after-hours isolation and containment without a full 24/7 service fee is huge.”
Tom Lovell,
Chief Technology Officer, Infinity Group
-
"As an MSP, having accurate threat detection paired with clear recommendations and automated remediation helps us respond faster and more effectively to security incidents."
Jean Ferreira,
IT Support Engineer, Simultech
Brandable one-pager
Your message to your customers
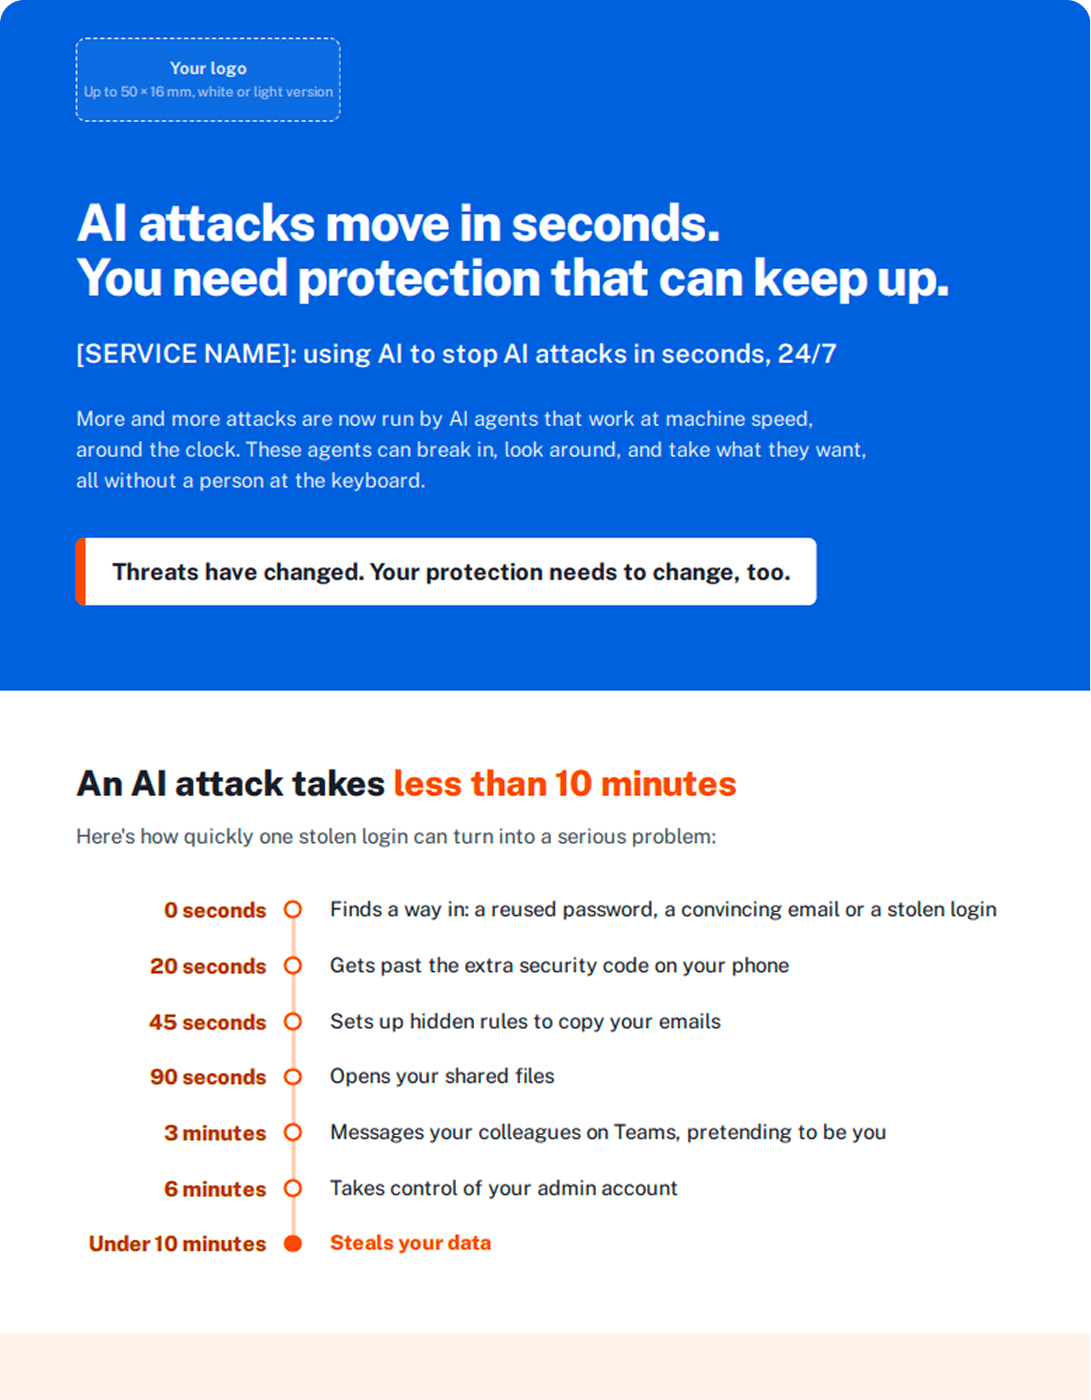
Download our brandable one-pager to help customers understand why agentic attacks are coming for small businesses and how your service keeps them protected around the clock.
What's inside:
- No-jargon talking points on why agentic threats make SMBs a target
- A ready-to-brand service description with space for your own service name
- Stats that land with SMB business owners to help you sell agentic TDR
- Comparisons of their current protection and Agentic TDR as a service
- An AI prompt to help you tailor the one pager to your branding in less than a minute